When an answer becomes an action
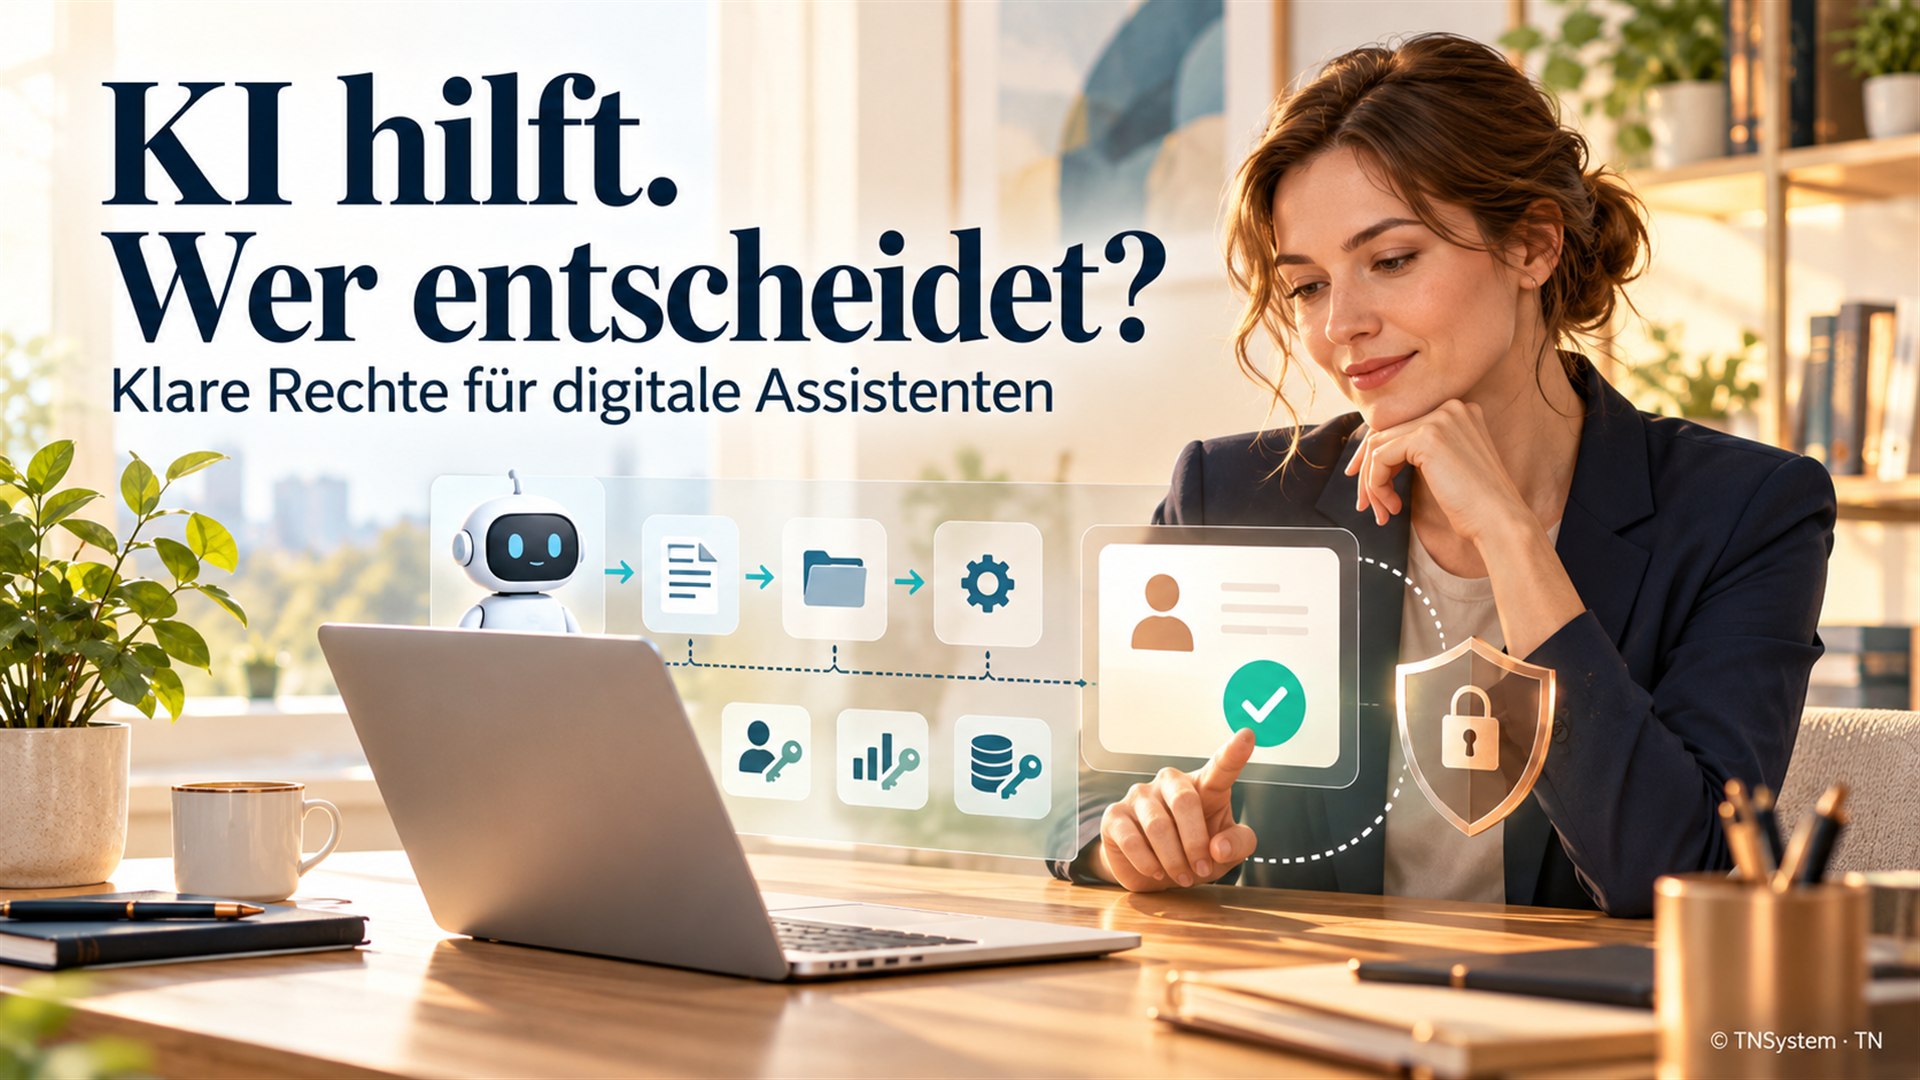
An assistant is asked to organise documents. May it delete originals? It prepares a quotation: may it send it too? It tests a software change: does it need access to the live customer environment?
To me, sensible agent use starts with these questions. Answer quality is not enough when a suggestion can become a real action.
What the current security report says
In a publication dated 23 October 2026, OpenAI explains stronger containment for internal training and evaluation environments, including layered controls and targeted testing. It explicitly distinguishes these research settings from customers' use of released models. [1]
That is not blanket evidence that an ordinary chat takes over personal systems. It is a reason to take technical capabilities and boundaries seriously.
Separate proposing, preparing and executing
I would divide a task into understandable stages. Reading information differs from changing files. Saving a draft differs from sending it to a customer. A local check differs from publication.
Each stage needs a clear decision-maker. Approval should identify a particular file, destination and effect. “Do whatever is necessary” is too vague on its own for consequential actions.
Limit permissions technically
I would give an assistant only the access its specific task requires. Test data and a separate workspace are often more appropriate than immediate access to production. An instruction alone does not replace technical permission boundaries.
External content needs particular care. A webpage or document being read must not, by itself, decide which access the agent receives. OWASP discusses least privilege, human approvals and separation of untrusted inputs among agent safeguards. [2]
Make stopping traceable
Before deployment, establish how running tasks can be stopped and completed actions reviewed. Stopping a job does not automatically undo earlier changes. A record should therefore distinguish planned, started, confirmed and failed actions.
Recovery needs planning too. A backup cannot make a recipient forget a message already delivered. Actions that cannot readily be reversed deserve deliberate approval.
My conclusion
A useful agent needs room to work, not unlimited authority. I would begin with a narrow scope, make effects visible and expand permissions only for specific tasks. This is neither a complete security architecture nor a guarantee against misbehaviour, but a better starting point than blind trust or a blanket ban.
Sources and context
Research date: 24 October 2026. Linked vendor and project information is not an independent product test. Examples and recommendations are identified as such.
[1] OpenAI: securing internal research environments, 23 October 2026
Read source ↗
[2] OWASP: AI Agent Security Cheat Sheet
Read source ↗