
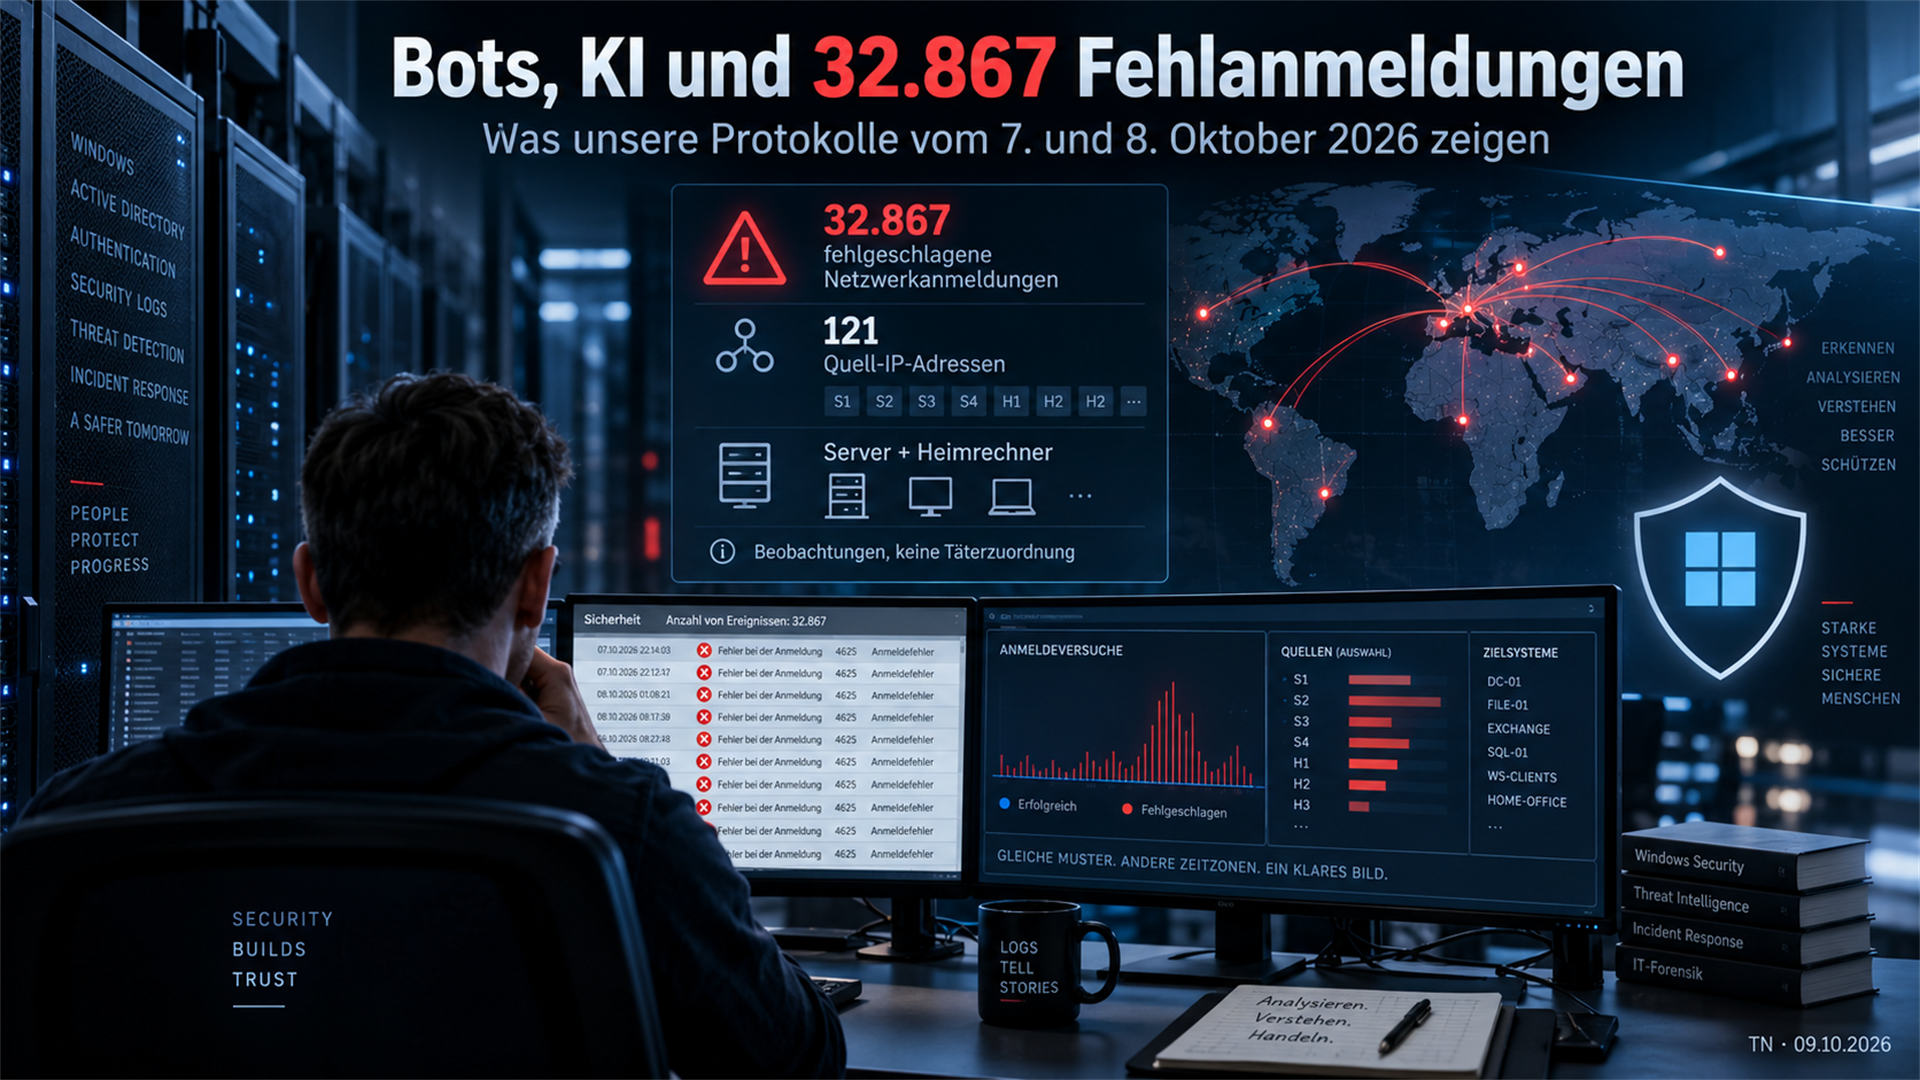
Observations from 7 and 8 October 2026
32,867 failed network logons from 121 different source IP addresses. These figures come from the supplied summary of our Windows server logs for 7 and 8 October 2026. Additional sequences of failed logon attempts were observed on a home computer. [1]
That is a reason to look more closely. It is not a reason to turn a log review into a story about supposedly all-powerful hackers.
The figures represent individual recorded failures. They do not mean that the same number of intrusions succeeded, or that every failure belonged to a separate attack campaign. The number of source addresses does not tell us how many people were involved either.
Above all, we have no evidence that artificial intelligence was used in the activity described here.
So why discuss bots and AI? Because these observations show where the discussion should begin: with traceable events, careful interpretation and the question of how to protect systems against repeated attempts to gain access.
What we actually observed
The following figures come from an extract of our security analysis. They are not a complete forensic examination of every system and access route.
We do not publish full IP addresses. Instead, we use source labels solely to distinguish entries within this article. We do not infer the identities of people, subscribers or companies from them.
Windows server: 32,867 failed network logons
S1: 7,944 recorded failed logons.
S2: 2,555 recorded failed logons.
S3: 1,280 recorded failed logons.
S4: 1,074 recorded failed logons.
The other 117 source IP addresses: 20,014 recorded failed logons.
Total across 121 source IP addresses: 32,867 recorded failed logons.
The four individually listed sources account for 12,853 failed logons. They are already included in the overall total. The remaining 20,014 events are the arithmetic difference between those entries and the overall summary. [1]
Home computer: additional sequences of failures
H1: 12 RDP authentication failures.
H2: 5 RDP authentication failures.
H3: at least 4,899 failed attempts.
These observations concern the home computer and are not part of the server total above. The two sets of findings are presented separately. [1]
For source H3, no successful access was identified in the reviewed extract. That statement applies only to that source and extract. It does not provide an all-clear for other periods, sources or access routes. [1]
A failed logon is not a complete account of an attack
A failed logon initially tells us that the particular authentication attempt did not complete successfully. Why it failed needs to be examined separately.
Microsoft's documentation for Windows event 4625, updated on 29 March 2026, explains the importance of the logon type, target account, source address, status and substatus. An unknown account, an incorrect password and an account lockout can represent different reasons for failure. [2]
Network logons and Remote Desktop access are not interchangeable terms. Microsoft distinguishes logon type 3, Network, from type 10, RemoteInteractive, used for remote interactive sessions through Terminal Services or Remote Desktop. Type 3 alone therefore does not establish a particular RDP access attempt. [2]
That is why we describe the server events as failed network logons and list the separately reported RDP authentication failures on the home computer on their own.
It is equally important to distinguish a blocked connection from a failed authentication. An authentication failure does not automatically mean that the firewall had already blocked the connection. A claim about the firewall's effect would require corresponding firewall records.
The figures are a starting point for investigation. They do not replace a review of individual events and their context.
Bots do not necessarily need AI
Ordinary programs can automate repetitive tasks, including repeated attempts to use credentials.
MITRE's Brute Force entry, updated on 12 May 2026, covers approaches such as password guessing, trying a small set of passwords against many accounts and using previously stolen credentials. None of those routines inherently requires a language model. [3]
Here, a bot means a program that operates automatically. A high failure count alone does not show whether its routine was fixed or included additional analysis.
The repetitions we observed are consistent with automated activity. They do not establish which tools were used or whether the sources were connected.
For a more precise interpretation, the intervals between events, target accounts and recurring failure patterns would be useful. Our summary does not include those details.
It would therefore also go too far to claim that a botnet had been proven. Many source addresses might belong to shared infrastructure, but their number alone does not establish that connection.
What AI can change about cyber attacks
On 7 May 2025, the UK's National Cyber Security Centre published an assessment of the cyber threat through to 2027. It expects AI to make existing steps in cyber intrusion more effective and efficient, including reconnaissance, vulnerability research, social engineering, basic malware generation and processing stolen data. [4]
This is not just about fully autonomous attacks. AI can assist with individual steps while people and conventional programs handle the rest. The NCSC identifies AI-assisted vulnerability research and exploitation as an important development. Its report is a general assessment containing forecasts, not an investigation of our systems. [4]
When assessing an incident, at least two questions should be kept separate: was the activity automated, and is there reliable evidence that AI was involved?
A deceptive message written with AI is different from an autonomous system selecting further attack steps. Calling both an “AI hacker” obscures that distinction.
What interests me most is whether our safeguards remain adequate when individual attack steps can be performed faster or with less effort. Whether a particular failed attempt came from an especially modern tool is secondary.
Why we do not publish full IP addresses
A source IP address initially identifies the observed technical origin of a connection. It does not prove the identity of the person responsible.
MITRE's documentation on multi-hop proxies, updated on 12 May 2026, describes how connections can be routed through intermediate systems, including compromised devices. The receiving system may see only the final hop. That is a general possibility, not a finding about the sources in our analysis. [5]
Publicly accusing someone solely on the basis of a source address would therefore be unjustified. The operator of the visible system might also be a victim of infrastructure misuse.
Privacy matters too. On 19 October 2016, in Breyer, C-582/14, the Court of Justice of the European Union held that dynamic IP addresses can be personal data for a website operator if that operator has legal means to identify the user using additional information. [6]
We do not need the full addresses for this article. Source labels are enough to explain the scale of the events and the limits of the review.
We therefore publish no alleged list of perpetrators, no identification of subscribers and no invitation to take action against particular systems. This article is intended to explain security issues, not to publicly accuse unknown third parties.
What matters when protecting systems
Our observations come from the environment covered by our security and firewall architecture. Detailed network plans, administrative access and complete rule sets are outside the scope of this article.
The following points are general matters to review. They are not claims about which individual control acted during the events described.
Limit exposure
The first question is which services actually need to be reachable from the internet.
CISA's StopRansomware Guide recommends closing unused RDP access, securing remote access, using multifactor authentication and recording RDP logon attempts. [7]
My first step would therefore be to compare existing access routes with actual needs. What is each connection for? Who may use it? What additional protection is in place?
A long list of blocked source addresses does not answer those questions. Nor does it automatically establish that the rest of the configuration is appropriate.
Count more than failures
A large number of failed logons is conspicuous. In an investigation, I would also check for unexpected successful logons in the relevant period.
Microsoft describes Windows event 4624, among others, as being generated when a logon session is created on the target system. [8]
That event alone does not prove an intrusion either. The question is whether the account, origin, time and logon type match expected operation.
The practical question is whether we can investigate unusual events in a traceable way. A display showing a large number is not enough. I want to understand why an event needs attention and who is responsible for following it up.
Prepare for recovery
Protection also includes knowing how to restore operations after a serious incident.
CISA recommends offline, encrypted backups of important data and regular recovery testing. Its guidance also emphasises keeping software and operating systems updated. [7]
For me, a backup is convincing only when the required data can actually be restored from it. A backup application's successful-job notification is just the first part of that check.
These basics may seem less spectacular than a new AI security product. I would still give them priority before introducing additional technology.
AI in defence: useful while control remains
AI can assist defenders too. On 21 September 2026, the NCSC discussed the potential and limitations of agentic tools in cyber defence. It distinguishes automatic detection from actions that directly affect production systems. Responsibility and possible operational consequences remain crucial. [9]
With large volumes of logs, I would initially use AI to support the review: organise events, suggest relationships and prepare questions for further investigation.
Every important conclusion would need to be traceable to specific data. Which events support the assessment? What information is missing? What alternative explanation is possible?
I would apply a much stricter standard once a system starts blocking accounts or changing configurations by itself. The NCSC discusses tightly bounded, controlled responses and the need to avoid business disruption. [9]
I would also minimise the data used in the review. To explain a general error type, I would start with a sanitised extract rather than transfer complete internal logs to an external service.
What follows from our observations
The summary for 7 and 8 October 2026 shows a substantial number of failed network logons on the Windows server reviewed. Additional sequences were recorded on the home computer. [1]
The figures warrant attention and careful investigation. They do not justify claiming that an AI attack has been proven, that every access route is secure or that every event has been fully explained.
I do not want to present them as a trophy for supposedly impenetrable defences. A high count of failed logons is not a complete security assessment.
What matters more is what we do with the findings: review necessary access, investigate unusual activity, assign responsibilities and prepare for recovery.
Whether an access attempt comes from a simple program, a bot or an AI-assisted tool, our task remains to protect our own systems in a traceable way and not confuse observations with assumptions.
Scope of this review
The internal figures are taken from the summary supplied for this article; the underlying raw logs were not independently re-examined during the editorial review. The observations apply only to the extract described, not to a complete forensic investigation. This article provides general information, not individual IT security or legal advice.
Sources and further reading
[1] TN security analysis: supplied summary of Windows server and home computer events for 7 and 8 October 2026. Non-public underlying data; full source IP addresses and internal configuration details are not published.
Public sources editorially checked on 9 October 2026. The CISA page could not be opened directly; its recommendations were available in the original-source search index.
[2] Microsoft Learn: 4625 — An account failed to log on. 29 March 2026.
Read source ↗
[3] MITRE ATT&CK: Brute Force — T1110. 12 May 2026.
Read source ↗
[4] NCSC: Impact of AI on cyber threat from now to 2027. 7 May 2025.
Read source ↗
[5] MITRE ATT&CK: Multi-hop Proxy — T1090.003. 12 May 2026.
Read source ↗
[6] Court of Justice of the European Union: Breyer, C-582/14. 19 October 2016.
Read source ↗
[7] CISA and partner agencies: #StopRansomware Guide.
Read source ↗
[8] Microsoft Learn: 4624 — An account was successfully logged on.
Read source ↗
[9] NCSC: One does not simply defend agentically. 21 September 2026.
Read source ↗
[7 additional] CISA: StopRansomware
Read source ↗